
One Server, Done Properly: A Debian Build You Can Audit
What "we take security seriously" actually looks like on a single Linux box: no shared root, every privileged action attributed, and logs that leave the machine before an attacker can.
Insights and articles
Development enhanced by AI
What "we take security seriously" actually looks like on a single Linux box: no shared root, every privileged action attributed, and logs that leave the machine before an attacker can.
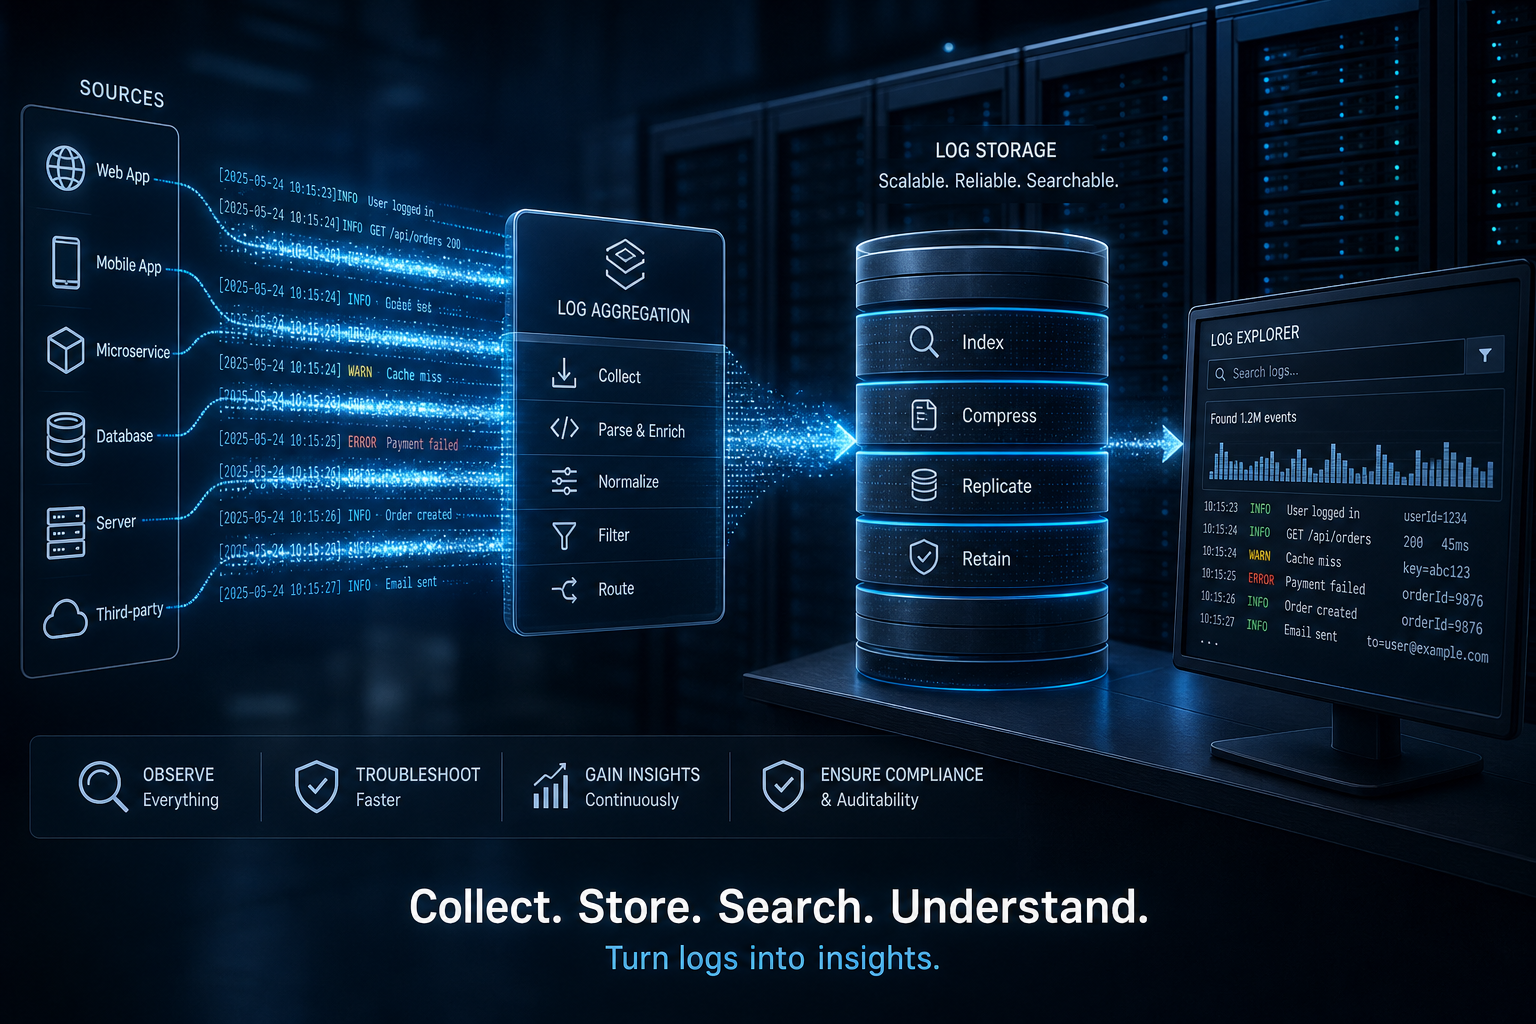
How to instrument a service so the people who have to read it later — on call, in an audit, during an incident — can actually find what they need.
A retail software team's perfectly-coded webhook module kept failing mysteriously every Monday—until they realized their metrics were measuring the wrong things and missing real-world problems.
vCPUs are just threads, cgroups don't replace the scheduler, and on NVMe the right I/O scheduler is usually 'none'. A ground-up tour of how Linux shares physical resources between virtual machines and containers — and which knobs are actually worth turning for small-to-medium workloads.
Graylog's volume-based pricing model hits small businesses hardest when they're least equipped to handle it—during critical early months when over-logging is essential for learning. Know what to negotiate before your sales call.